
Privacy and Accountability
Privacy in design. Responsibility in operation.
Law, architecture and day-to-day practice have different roles. Softa’s approach connects the purpose of processing with access, retention, user rights and accountable service delivery.
Design and default
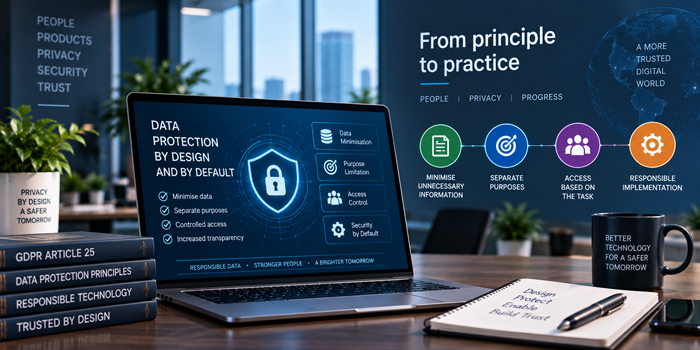
GDPR Article 25 establishes data protection by design and by default. The EDPB’s guidance connects that responsibility with effective implementation of data-protection principles, not merely a consent banner or encryption setting. The relevant actor and processing determine the concrete duties.
Softa’s architectural direction is to minimise unnecessary information, separate purposes and keep access connected to the task. This is a design relationship to the legal principle, not a claim that the company’s systems have received a general GDPR certification.
India’s staged DPDP framework
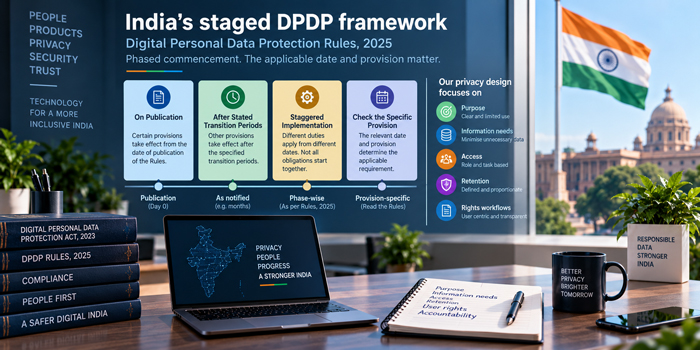
The notified Digital Personal Data Protection Rules, 2025 provide phased commencement: different provisions take effect on publication or after stated transition periods. The applicable date and provision matter. Notification of the rules does not mean every duty commenced at the same time.
The company’s privacy design addresses purpose, information needs, access, retention and rights workflows. Actual service notices and procedures must reflect the relevant processing and legal obligations. This overview does not declare every product legally compliant merely because those concepts appear in its architecture.
AI and synthetic media
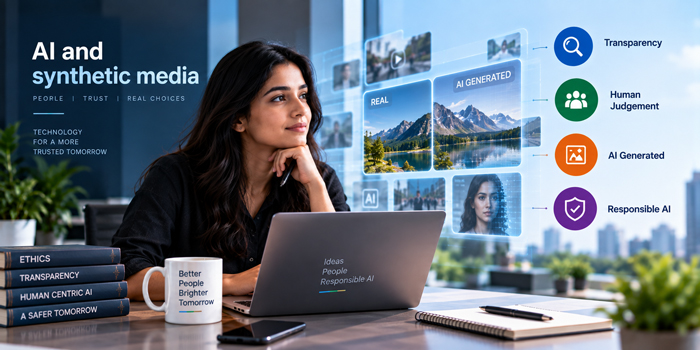
The EU AI Act uses a role- and risk-based framework. Its transparency provisions address, among other matters, informing people about certain AI interactions and identifying or labelling certain AI-generated content. Provider and deployer responsibilities, exceptions and the relevant use case remain important.
Softa’s approach to AI and media distinguishes the right to use a source, the permission to retain information and the authority to act. Synthetic identity raises a separate question of representation: an illustration is not evidence that a person, event or deployment exists.
The service-specific account
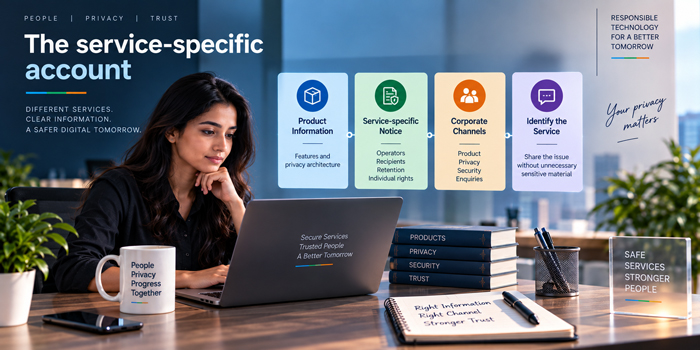
The product pages explain privacy architecture. Service-specific information about operators, recipients, retention and individual rights belongs to the applicable product notice. Website Privacy describes the separate data practices of this downloadable website.
Product, privacy and security enquiries can begin through the published corporate channels. A request should identify the service and issue without sending unnecessary sensitive material. The actual operational relationship, not this high-level description, determines the applicable procedure.